• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
TheWayoftheWeb

TheWayoftheWeb

Content and Digital Marketing Specialists

  • Blog
  • The Cipher
  • About Us
    • Useful Resources For Businesses In Peterborough, UK
  • Contact Us
  • Show Search
Hide Search

wordpress

WordPress Update Error: Download failed.: Failed to write request to temporary file

May 8, 2016 By Dan Thornton

We currently manage around 35 WordPress installations and websites for a variety of clients and my own projects. I originally started using WordPress for my own websites around 10 years ago, and over time I’ve arranged a range of hosting, themes and plugins that I know I can trust.

When I recently updated to the latest version of WordPress, I received the following error message: WordPress Update Error: Download failed.: Failed to write request to temporary file.

Strangely it only occurred on one of my sites from the 35 I updated, and it’s a site which has run without issue for several years. It’s an error message I couldn’t remember seeing before, so it was time to do some investigating. And it’s why I’ve written this post as a reminder if it occurs again.

Fixing_Wordpress_Error_Failed_Temporary_File


WordPress Update Error: Download failed.: Failed to write request to temporary file

The error message appears when you attempt to automatically the core WordPress files, plugins or themes on the affected website. There’s no other information to accompany the message, and it appears there are various ideas as to what may cause it. The most common reason given is that the WordPress update will place temporary files in a directory on your server which isn’t specific to WordPress. That’s normally limited in terms of space by your website host, and it appears that a full temporary file may trigger the error.

Generally old files should be cleared out of the folder automatically, but that doesn’t always happen. So over the course of time, it can become full.

However there are some questions about this – contacting my website host for that particular site via support indicated that the temporary folder was only 5% full. That may have been because I’d completed the required updates via a workaround (details below), but it may indicate there’s another issue.

The other suggestion is a server configuration issue which means it’s not set up to properly use a temporary folder, which also makes sense. It could occur on an existing site if something has been changed by your website hosting provider for that particular server.


Fixing Failed to write request to temporary file:

So there are several things you can try:

  • Check whether there is any issue with space on your server or via your cPanel account.
  • Clear out the temporary directory of any files you know are no longer required.
  • Check and alter the user permissions for the WP-Content folder via your cPanel to have chmod 755
  • Edit the wp-config file to add a new line of code.

It was editing the wp-config file that immediately solved my own issue.
Two important things to note:

  • Before you make any changes or delete anything, it’s best to back things up. Some of the files in your temporary directory may relate to website stats software or have other uses which means you’ll need to keep them.
  • If you’re adjusting user permissions or editing your wp-config file, it can be a security risk, so make sure you switch them back afterwards.


Server Space and Set-Up:

Even if you can access your temporary folder (e.g. /tmp) via ftp, you may not be able to actually edit or delete anything. Particularly if you’re on shared servers (the most common set-up for lower priced hosting, including for most blogs etc). So you’ll need to contact your website hosting provider or raise a support ticket.

I pick my hosting based on the speed and quality of their product and their customer support, so I had a reply within an hour on a Sunday morning. But as the WordPress update was security based (and I tend to be a curious fellow), I didn’t want to wait while they responded, so I moved onto the next step.


WP-Content chmod 755:

The chmod setting controls who can Read, Write (delete and add folders) and Execute (run scripts) to folders on your website. Generally by default you want to have access to change things without letting anyone else make edits. Which is why generally your WP-Content folder should be set to chmod 755

To check, log into your website hosting provider, and navigate to your File Manager. Generally you’ll be able to see your chmod settings there and change them if necessary. One suggested solution is to temporarily change the WP-Content folder to chmod 777 which allows anyone to upload to it – obviously this is a massive security risk, so if you try this, change it back afterwards immediately!


Edit WP-Config:

So, first you need to open up your File Manager in your web host cPanel, or get into your site via ftp.

Locate your wp-config.php file.


It should look something like the following, with the name of your Database in it:

* @package WordPress
*/

// ** MySQL settings – You can get this info from your web host ** //
/** The name of the database for WordPress */ define( ‘DB_NAME’, ‘database_name_here’ );

/** MySQL database username */ define( ‘DB_USER’, ‘username_here’ );
/** MySQL database password */ define( ‘DB_PASSWORD’, ‘password_here’ );

/** MySQL hostname *
/ define( ‘DB_HOST’, ‘localhost’ );


All you then need to do is add the following, before the MySQL details:

define(‘WP_TEMP_DIR’, ABSPATH . ‘wp-content/’);


So it will look something like:

* @package WordPress
*/
define(‘WP_TEMP_DIR’, ABSPATH . ‘wp-content/’);

// ** MySQL settings – You can get this info from your web host ** //
/** The name of the database for WordPress */ define( ‘DB_NAME’, ‘database_name_here’ );

/** MySQL database username */ define( ‘DB_USER’, ‘username_here’ );
/** MySQL database password */ define( ‘DB_PASSWORD’, ‘password_here’ );

/** MySQL hostname *
/ define( ‘DB_HOST’, ‘localhost’ );

Then just save, close, and try to run your updates again.


When it’s all fixed:

When all the required updates have run, make sure you reset any changes to your chmod permissions, and also remove the line of code from WP-Config.

Even if you’ve managed to solve the problem via those workarounds, it’s worth contacting your website hosting provider to see whether the /tmp file needs clearing, or if there’s a server configuration problem. Otherwise you’ll need to go through making the changes for every update in the future, and it’s very easy to accidentally leave your modified wp-config file live after the umpteenth update.

 

Security Update for Jetpack WordPress Plugin

April 11, 2014 By Dan Thornton

Joining the news of the Heartbleed vulnerability that affects much of the internet, and a security update for WordPress itself, now comes the news that there is a critical security update for the Jetpack WordPress plugin.

Jetpack 2.9.3 contains a fix for a bug which allows an attacker to bypass access controls and publish posts, which could be combined with other attacks to escalate access. It’s existed since the release of Jetpack 1.9 in October 2012, and as yet there is no evidence of it being used in the wild.

JetpackLogo

However, now it has been made public, you need to make sure your site is updated asap – the team behind Jetpack have been working with hosting and network providers to reduce the problem, and have made updated releases for all 11 vulnerable versions of Jetpack from 1.94 through to 2.9.3.

So if you’re running Jetpack on one or more of your sites, make sure you’re either updating it now through your WordPress dashboard, or visit the Jetpack site to manually grab the updated releases and install the appropriate one for your website.

WordPress 3.8.2 now available to download and install

April 8, 2014 By Dan Thornton

The latest version of WordPress is now available to download and install. It’s an important security release which solves some important security issues, along with fixing a number of bugs.

WordPressLogo

The security list is:

  • Potential authentication cookie forgery. CVE-2014-0166.
  • Privilege escalation: prevent contributors from publishing posts. CVE-2014-0165.
  • (Hardening) Pass along additional information when processing pingbacks to help hosts identify potentially abusive requests.
  • (Hardening) Fix a low-impact SQL injection by trusted users.
  • (Hardening) Prevent possible cross-domain scripting through Plupload, the third-party library WordPress uses for uploading files.

There’s more information available in the WordPress Codex. If you’re already allowing automatic updates, the release will apparently install throughout the next 12 hours, or you can update manually now. As always, before any significant WordPress or plugin update, it’s always best to back up your site.

WordPress Automatic Updates – Good or Bad?

February 5, 2014 By Dan Thornton

Automatic updates were introduced to WordPress with the 3.7 Basie release, but the debate about them has been re-ignited as they recently came into effect for a large number of users who found their websites moved from 3.8 to 3.8.1 without any prior notification.

As much as I like and respect his WP knowledge, I’m forced to disagree somewhat with Rhys Whynne’s article, which says they’re an unqualified good thing, and side with the view he references from Marj Wyatt. The way that automatic upgrades have been implemented without any easy controls for website owners means that many people will need to either install an extra plugin or add code manually to stop their sites from being changed without their knowledge.

WordPress-Automatic-Updates

WordPress Auto Updates: The Benefits

There are several positives to having automatic upgrades for security reasons and minor releases. The first is that many, many people around the world are using outdated versions of WordPress and associated plugins which is a major security risk for them. Outdated software is a great way to invite hackers to easily get into your site, particularly if it allows them to use widely accessible and known vulnerabilities which can be hit in bulk.

And having worked with the large number of sites we develop, host and manage for clients, I can say that most are updated infrequently at best.

It also means that users aren’t paralysed by fear when given the option to upgrade. It also saves the cost of paying for anyone to simply have the confidence to perform a site back up and click yes to upgrade (Which is why we’ve always installed auto-backup tools for clients).

In terms of connectivity, even if the WordPress server has issues during the upgrade process, it won’t affect your site. If it fails, the site falls back to the normal state anyway.

And although I personally like to have as much control over any software updates and upgrades, in terms of trusting the intentions of WordPress, I’m more comfortable with an open source and fairly open organisation having the right aims than many of the other software platforms and products we all use on a daily basis.

WordPress Auto Updates: The Problems

So why wouldn’t I just recommend everyone lets Automatic Updates do their job?

Firstly, there is an ownership issue. Although I accept Rhys’s point that auto updates will reduce security issues for which WordPress could incorrectly be blamed, the fact is that the websites being updated are not the property of WordPress, are not on WordPress owned servers, and aren’t the responsibility of WordPress. Unless they’re also intending to come and help if I make a mistake while I’m tweaking some CSS as well?

But more importantly from a day-to-day practice is that minor updates can have major consequences. Although plugins and extensions should be designed and built in a way which means minor updates don’t affect them, that’s asking third party developers to predict the future. And the further you extend WordPress, the more risky it is.

Plus the time, resource and financial cost of ensuring everything is working can be problematic. It requires every third party supplier to be ready for every beta test and notification of an impending update, and to be able to test every single product they list prior to the update occurring.

Having worked with plugins like Jigoshop, that means not only the Jigoshop core plugin, but potentially checking tens of themes and hundreds of extensions, which have been created by a large number of suppliers.

The majority of people involved in that project, and many others, are making that effort, but it takes time and co-ordination – with an almost infinite combination of hosting, server setup, conflicting plugins and extensions etc.

And when we update a site, we always schedule it for the time which causes least disruption to site owners and their customers. That’s difference for every business, so there’s no way for WordPress to achieve this without looking at the website analytics for 1 million+ websites at a time.

That’s why I believe it’s wrong to have introduced Automatic Updates without any manual controls for a user or administrator which don’t require either coding or installing yet another plugin.

WordPress Auto Updates: Our Advice

One thing we can all agree on – make back ups of your site often. Rhys recommends once per day, which we’d recommend for sites which are critical to you and your business, although it’s really a question of how much you’re prepared to loss in a disaster versus the cost of storage space.

If your site is fairly simple, using core WordPress functionality and a handful of plugins, then Auto Updates are pretty much fine. For instance, I have no issue with having them enabled on www.danthornton.net as it’s a personal blog with very few tweaks or plugins.

If your site is complex, and uses substantial plugins or extensions, then we’d recommend turning off Auto Updates, which is what we’ve done for various clients. We’re not willing to let anything be changed on those sites without the opportunity to test and double check it.

If your site access is essential for your business, then we’d recommend turning off Auto Updates. Although maintenance mode passes very quickly, you want to be able to experience any issues at a time when you least disrupt customers and you’re on hand to fix any issues, rather than while you’re in a meeting, on holiday or sleeping.

WordPress Auto Updates: Turning them off

There are two ways to re-assert your control if you want to disable or restrict the automatic updates. The first is to edit the code on your site, and the instructions are available on the WordPress Codex. The second is to use one of the various plugins which have sprung up to offer similar functionality, such as ‘Update Control‘.

So far we’ve yet to test the plugin options, and have installed the manual option across a range of client sites to avoid adding plugins which shouldn’t be necessary.  Essentially you’re then updating an additional plugin to cope with the update functionality WordPress introduced to avoid having to update so often.

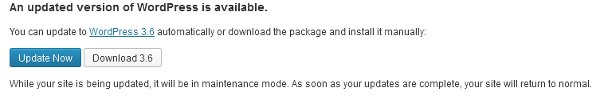
WordPress 3.6 is now available

August 2, 2013 By Dan Thornton

The latest version of WordPress, which is version 3.6, is now live with some new functions and features. As always, we’d recommend backing up your site before starting any upgrade procedure, which is a process we undertake for many of our clients.

The release is codenamed ‘Oscar’:

Features for WordPress users:

For general users and authors, the main features of the new release are:

  • New Twenty Thirteen default theme.
  • Revamped Revisions to save every change with a new interface
  • Post Locking and Augmented Autosave to allow saves by authors and taking over post editing when more than one author is working on an individual post.
  • Built-in HTML5 media player for native audio and video embeds.
  • Improved integrations and oEmbed support for Spotify, Rdio and SoundCloud.
  • Easier Menu Editor.

Developers also benefit from a new audio/video API with access to metadata like ID3 tags, HTML5 markup for more elements, better filters for revisions, and a long list of additional changes.

WordPressUpdate

We’ve already updated this site to 3.6 and some other test sites, and haven’t experienced any substantial problems. But it will depend on the plugins and frameworks you are currently using, so please do make sure you back up before updating, especially if you don’t have regular backups already taking place.

  • Page 1
  • Page 2
  • Page 3
  • Interim pages omitted …
  • Page 6
  • Go to Next Page »

Primary Sidebar

Join us…

  • Facebook
  • Instagram
  • LinkedIn
  • RSS
  • Twitter

We only exist to deliver results for your business. So you get fresh Content, expert SEO, engaging Social Media, or a new Website which is right for you – and your customers.

We help you build your brand, reach more customers and increase your revenue

Search

Categories

Creative Commons License
This work by TheWayoftheWeb is provided under a Creative Commons Attribution-NonCommercial-ShareAlike 4.0 International License.

Start growing your business today Contact Us

Recent Comments

  • Don't wait for your ship to come in... - TheWayoftheWeb on Freelance & Consultancy

TheWayoftheWeb

Copyright © 2026· TheWayoftheWeb Ltd. Company Number 08038527. ICO registration: ZB397650